Topic: Responsible AI Governance: What GRC Leaders Need to Know
Abstract: As AI moves rapidly from experimentation to enterprise-wide adoption, organizations face a growing challenge: enabling innovation while maintaining effective governance, risk management, and compliance. For GRC leaders, AI governance is becoming an essential extension of enterprise risk and compliance rather than a standalone technology issue. The current webinar explores what security leaders need to know to establish a practical approach to responsible AI governance. The session will examine the key risks associated with AI systems, including data privacy and security, bias, lack of transparency, model reliability, third-party dependencies, and the growing use of autonomous and agentic AI.
The webinar will also cover the importance of clear accountability, policies, controls, human oversight, and evidence-based reporting. Organizations need a practical leadership perspective on moving beyond AI principles to an actionable, measurable governance structure aligned with business objectives, so they can adopt AI responsibly while maintaining trust, resilience, and regulatory readiness. Join us to gain insights into how existing GRC capabilities can be adapted to govern AI across its lifecycle, from initial use-case assessment and risk classification to implementation, monitoring, and ongoing assurance.
Key Takeaways:
- Principles of responsible AI and their relevance to enterprise governance, risk, and compliance
- Understanding key AI risk areas, such as data privacy, security, bias, transparency, and reliability
- Extending existing GRC frameworks to govern AI across its lifecycle
- Approaches to AI risk assessment, classification, control design, and continuous monitoring
- Importance of defining clear ownership, accountability, and human oversight for AI-driven decisions
- Creating evidence-based AI governance that supports internal assurance, audits, and regulatory requirements
- How security leaders can balance AI innovation with risk management, trust, and compliance
Speaker:
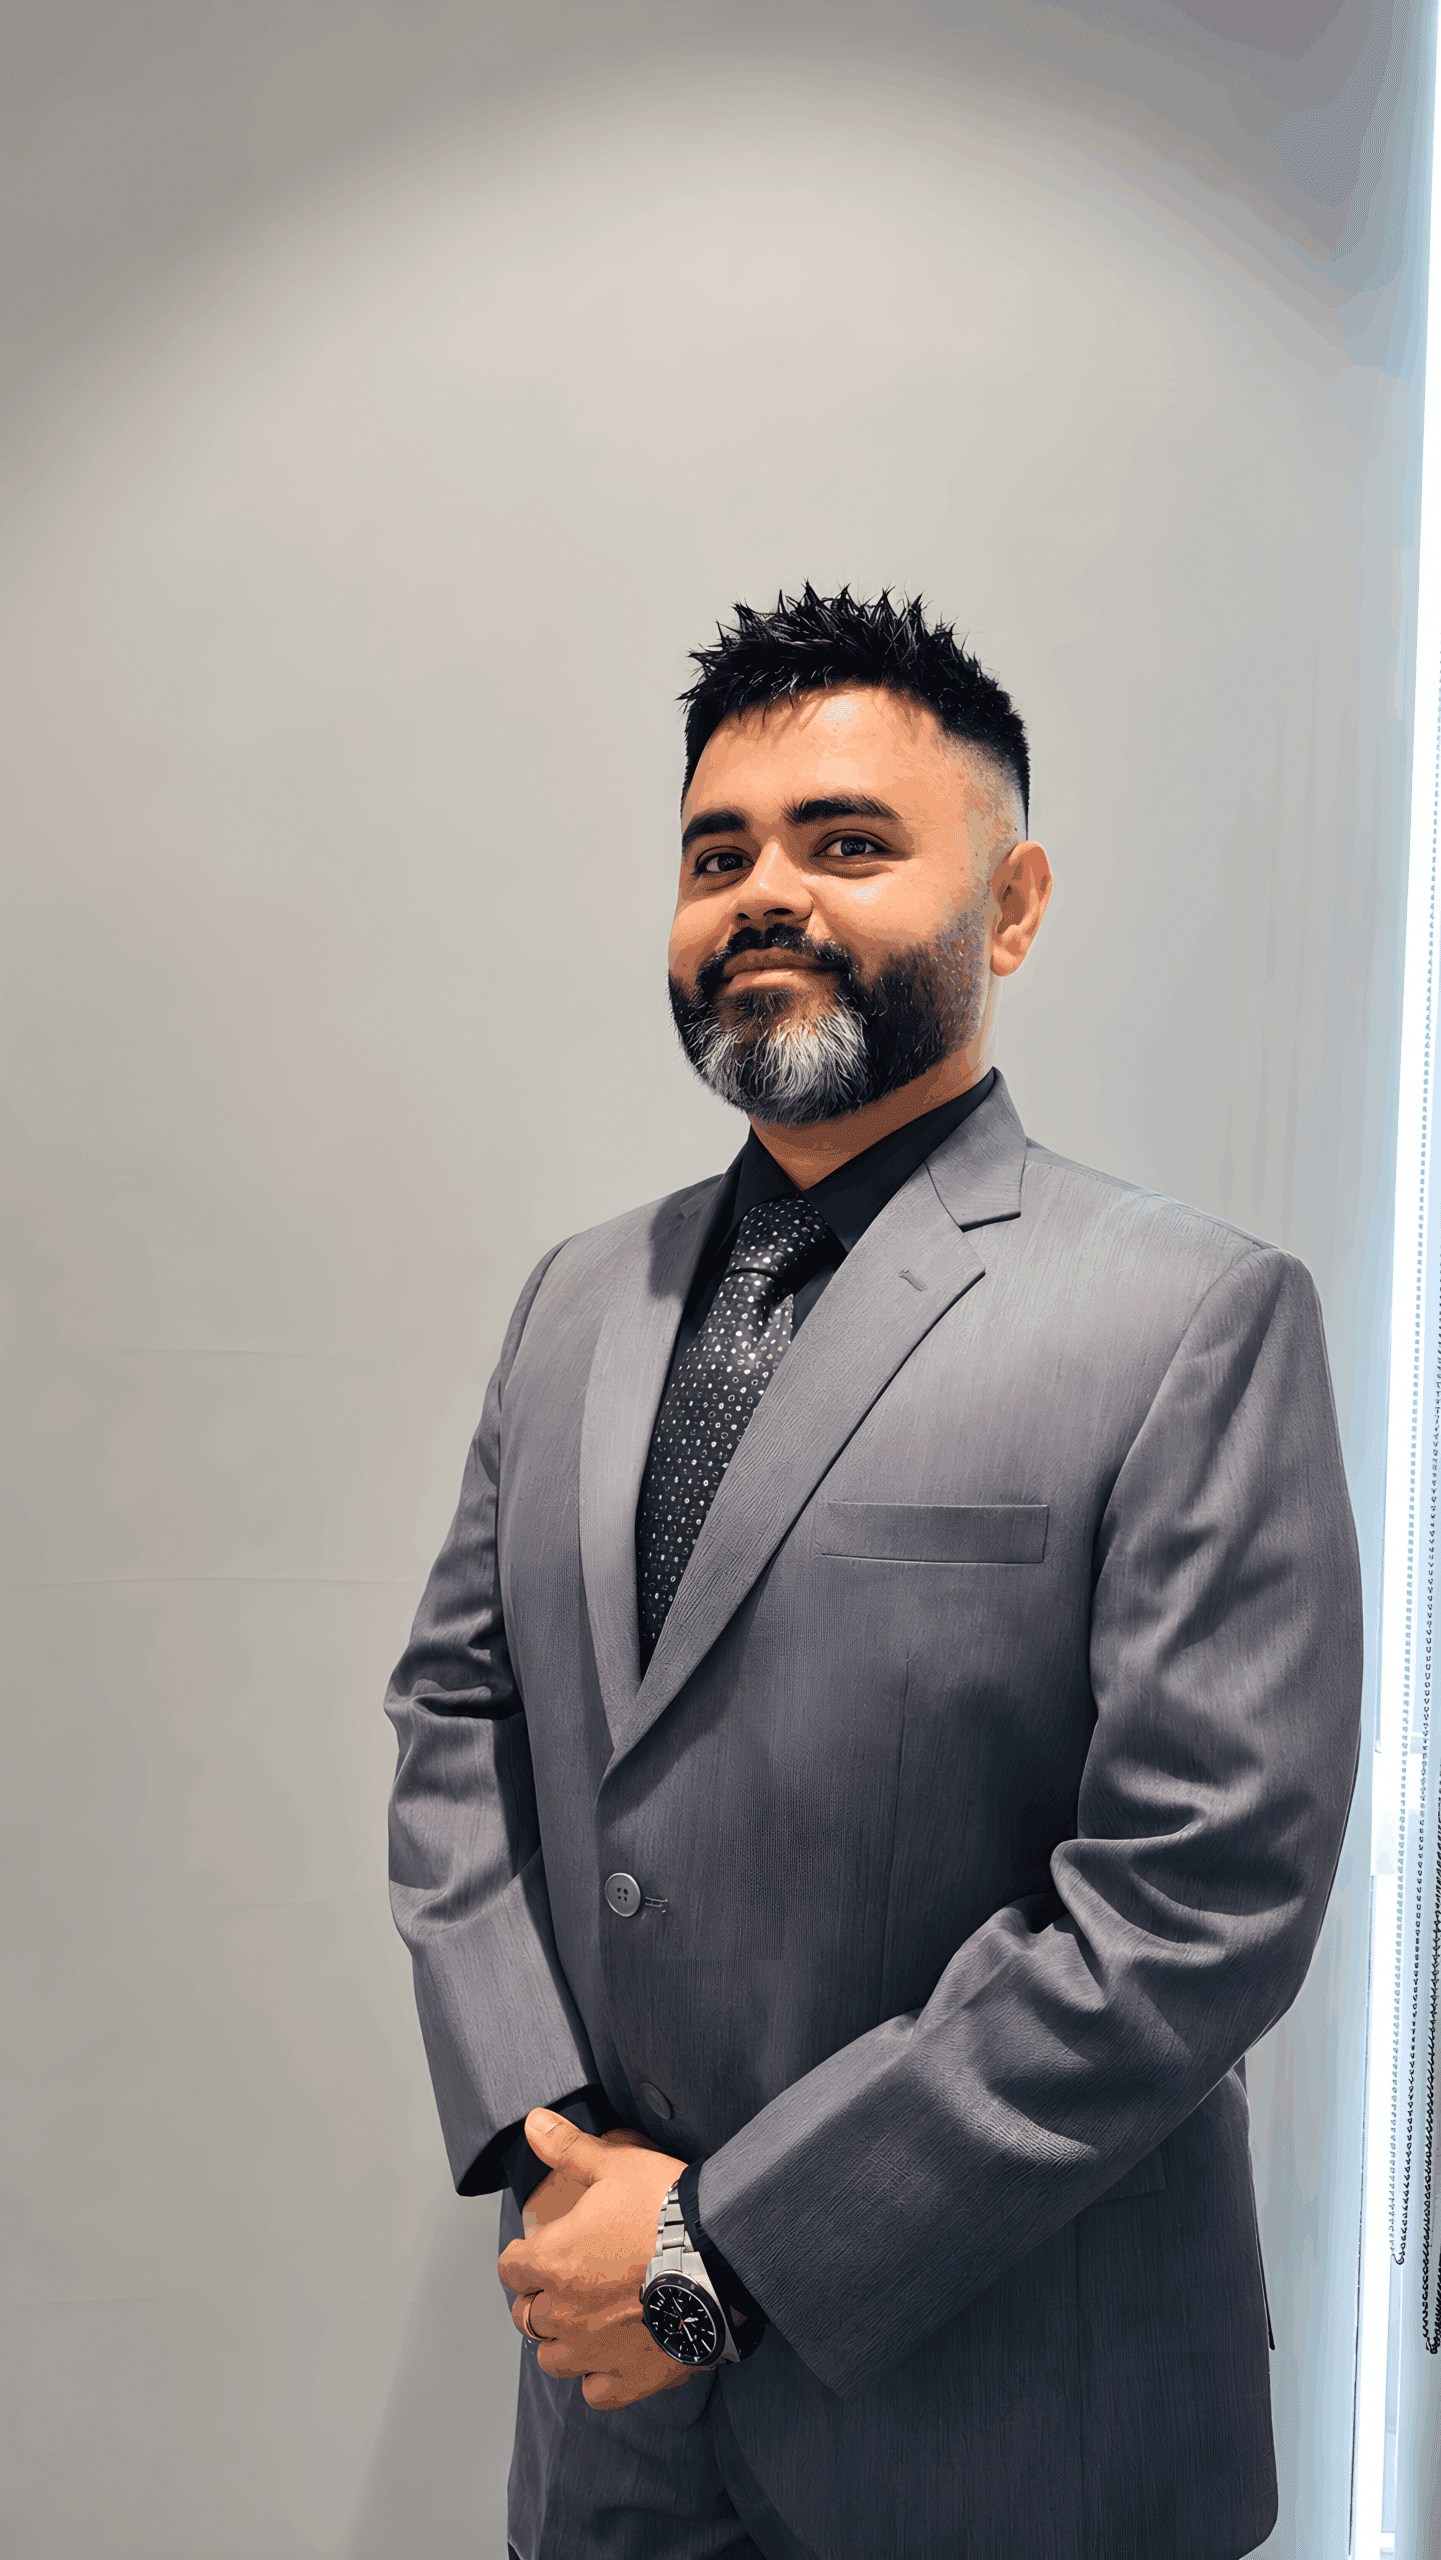 Joel Rosario Pereira, Cybersecurity Leader, International Organization in the BFSI Sector, Ex-Big Four consulting
Bio: Joel Pereira is a seasoned cyber, information security, and AI governance leader with more than 12 years of international experience driving cybersecurity governance, regulatory compliance, enterprise risk management, and responsible technology transformation.
With experience spanning leading global organizations including Deloitte, PwC, KPMG, and an international group in the BSFI sector, Joel has advised organizations across the Middle East in financial services, government, and other critical sectors. He brings a unique ability to bridge business strategy, technology, regulatory expectations, and cybersecurity governance.
Joel has led enterprise-wide initiatives covering information security strategy, NIST Cybersecurity Framework assessments, ISO/IEC 27001 certifications and SOC 2 attestations, regulatory engagement, cyber resilience, and security culture. More recently, he has been instrumental in establishing enterprise AI governance capabilities and alignment with regulatory expectations for the responsible adoption of AI.
He holds an MBA in Global Finance & Banking and a B.E. in Computer Engineering, along with globally recognized certifications including AIGP, CISSP-ISSMP, CISSP, CRISC, CCSP, CISM, CISA, PMP, various Microsoft certifications, and CDPSE.