Topic: Digital Forensics and Incident Response: From Incident to Evidence Analysis
Abstract: When a cybersecurity incident occurs, the ability to respond quickly while preserving reliable evidence can determine how effectively an organization contains the threat, understands what happened, and prevents recurrence. Digital Forensics and Incident Response (DFIR) brings these capabilities together, enabling security teams to move from initial detection and containment to evidence collection, analysis, and post-incident investigation. This webinar provides a practical overview of the DFIR lifecycle, covering the critical steps involved in responding to a security incident and conducting a structured forensic investigation. The discussion will explore first-response procedures, evidence identification and preservation, forensic acquisition, analysis of endpoints and network activity, timeline reconstruction, and the identification of indicators that can reveal attacker behavior. The session will also examine the importance of chain of custody, documentation, forensic integrity, and investigative processes when evidence may need to support internal investigations, audits, regulatory requirements, or legal proceedings. Participants will gain insights into how organizations can establish repeatable DFIR processes that improve investigation speed, evidence quality, and overall incident response effectiveness.
Key Takeaways:
- Understanding the Digital Forensics and Incident Response (DFIR) lifecycle.
- Essential steps for first response, incident triage, containment, and evidence preservation.
- Best practices for forensic acquisition and maintaining evidence integrity.
- Analyzing endpoints, network, system, and application artifacts during an investigation.
- How timeline analysis and correlation of forensic evidence help reconstruct attacker activity.
- Importance of chain of custody, documentation, and forensic procedures.
- How DFIR teams can use investigation findings to support incident response, threat intelligence, compliance, and remediation.
- Building repeatable and defensible DFIR processes to improve organizational readiness and resilience.
Speaker:
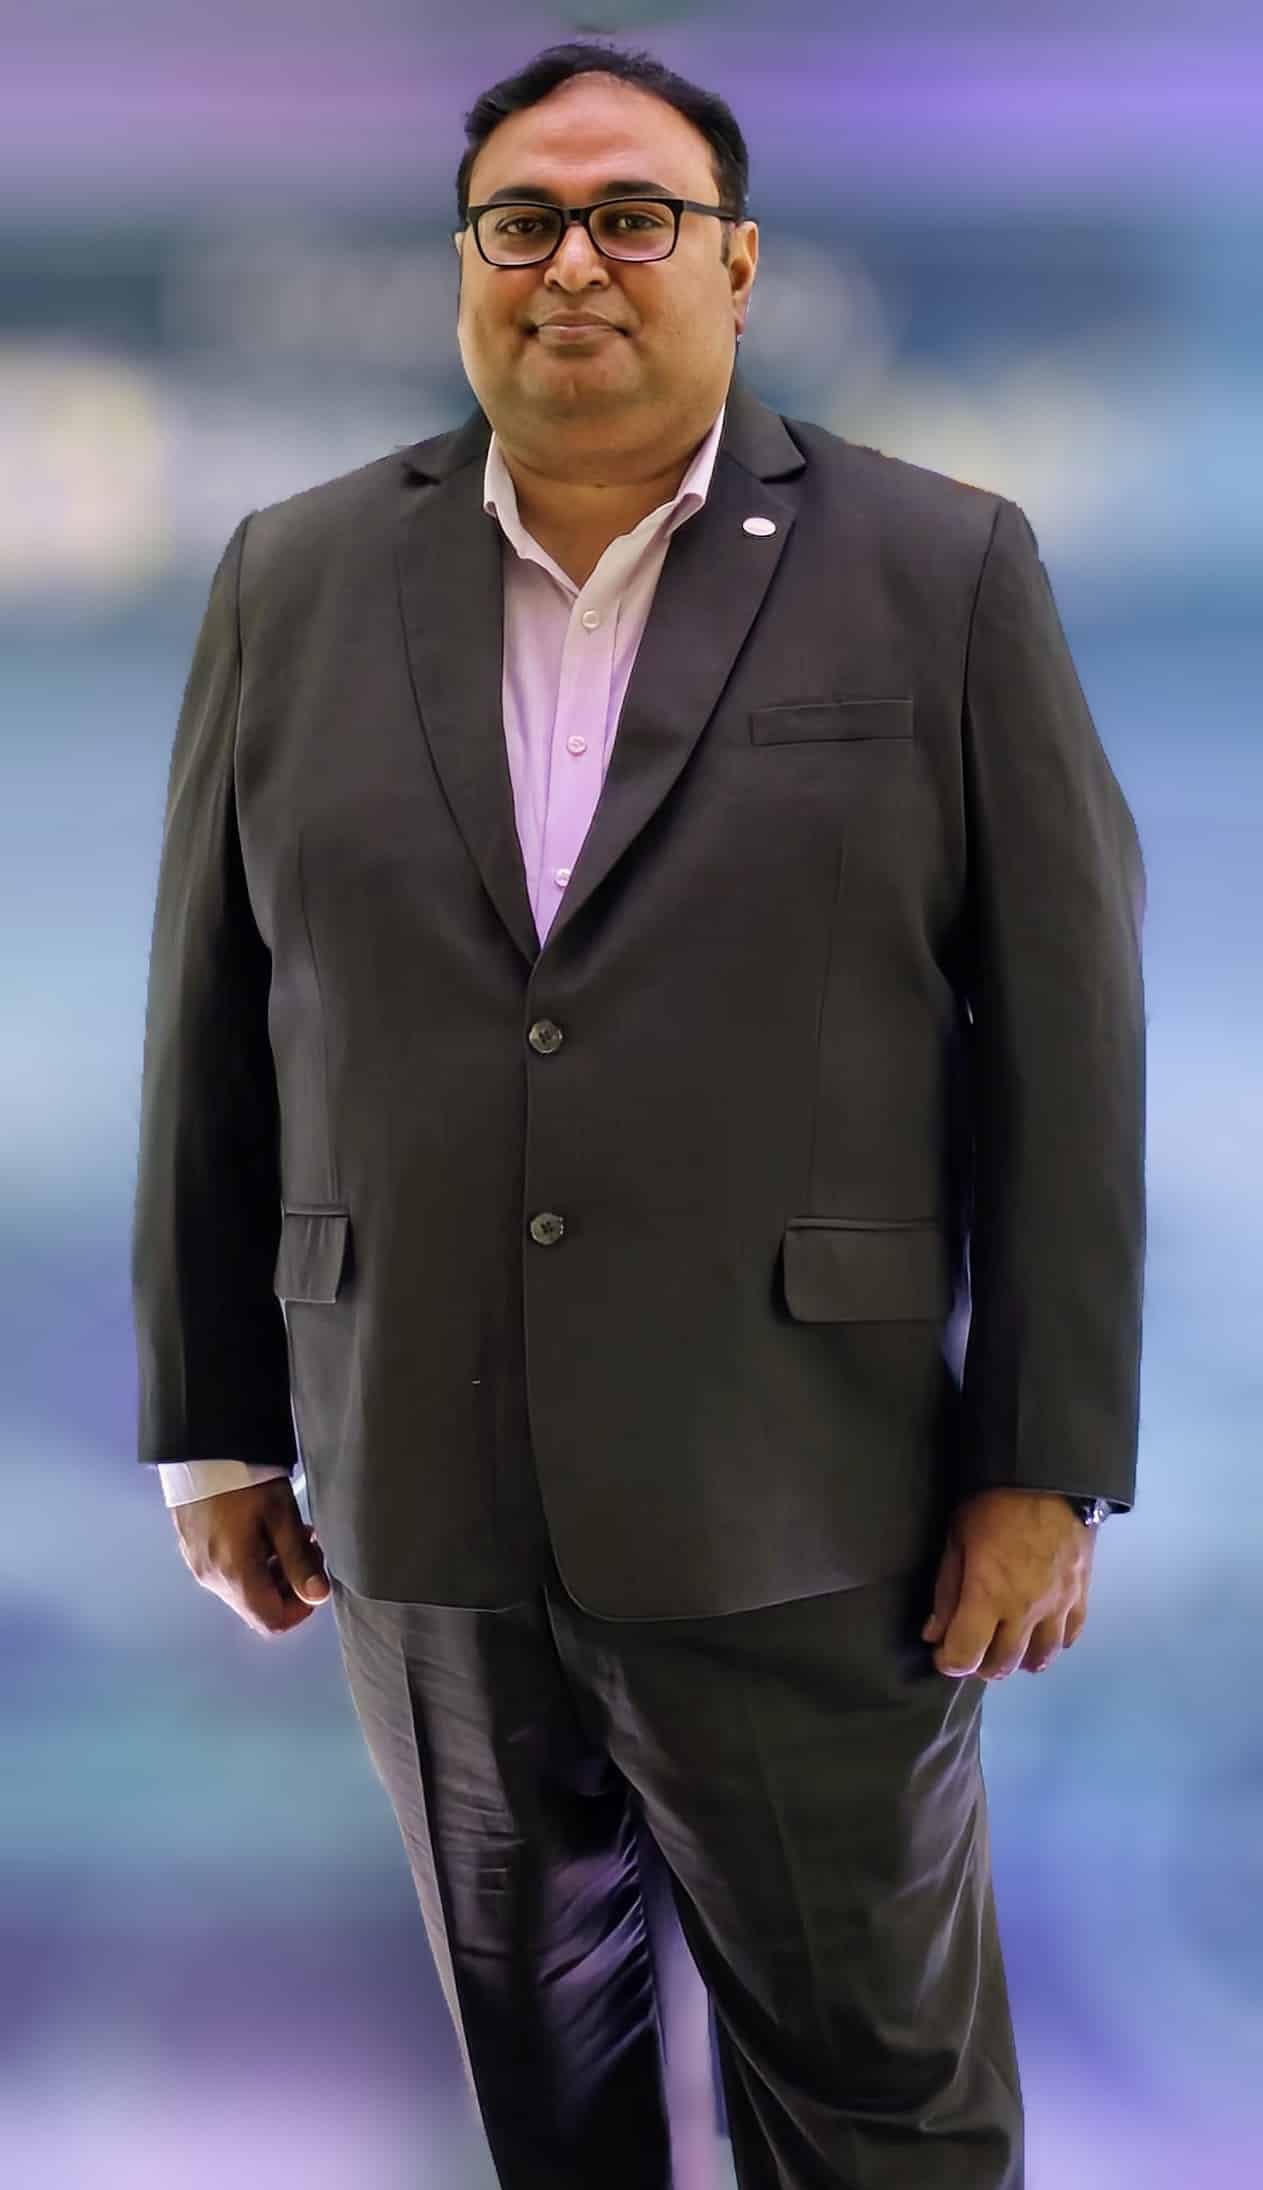 Harinderjeet Singh Walia, Senior Regional Manager, Critical Incident Response, Forcepoint
Bio: Harinderjeet Singh Walia brings more than 25 years of cybersecurity experience gained across high-security environments, including a distinguished career as a veteran of the Indian Air Force. His background spans critical information infrastructure protection, enterprise-wide security transformation, and leading incident response operations at scale.
With deep expertise across AI, penetration testing, digital forensics, threat intelligence, and enterprise security architecture, he has built a reputation for developing robust defenses against sophisticated and evolving cyber threats. Beyond his technical work, Harinderjeet is committed to developing the next generation of cybersecurity professionals, helping them align security strategy with both business objectives and regulatory requirements.