Topic: Governance, Risk, and Compliance in Action: Proving Security Outcomes
Abstract: Governance, Risk, and Compliance (GRC) is increasingly moving beyond policies, frameworks, and compliance checklists toward demonstrating measurable security outcomes. For security leaders, the challenge is no longer simply proving that controls exist, but demonstrating that they are effective, risks are understood, and investments are delivering tangible improvements in organizational resilience. The current webinar explores how organizations can transform GRC from a compliance-driven function into a strategic capability for measuring and communicating security outcomes. It will examine how security teams can connect governance requirements, risk assessments, control effectiveness, and compliance activities to real-world security performance. The webinar will focus on practical approaches to establishing meaningful metrics, mapping controls to business risks, measuring control effectiveness, identifying gaps, and creating evidence that can withstand regulatory and audit scrutiny. It will also explore how automation, continuous monitoring, and data-driven reporting can help organizations move from periodic compliance assessments toward continuous assurance. Join us to gain a perspective on how to communicate security outcomes in business terms that help board members and executives understand not only organizational compliance but also the actual security posture.
Key Takeaways:
- Transforming GRC from compliance checklists to measurable security outcomes.
- Connecting business risk, security controls, compliance requirements, and security performance.
- Identifying meaningful GRC and security metrics that demonstrate control effectiveness and risk reduction.
- Approach to measuring and proving control effectiveness rather than simply documenting the existence of controls.
- Understanding how continuous monitoring and automation can strengthen assurance and reduce manual compliance effort.
- Building audit-ready evidence and maintaining visibility into security posture throughout the year.
- Role of outcome-based GRC towards risk-based decision-making.
Speaker:
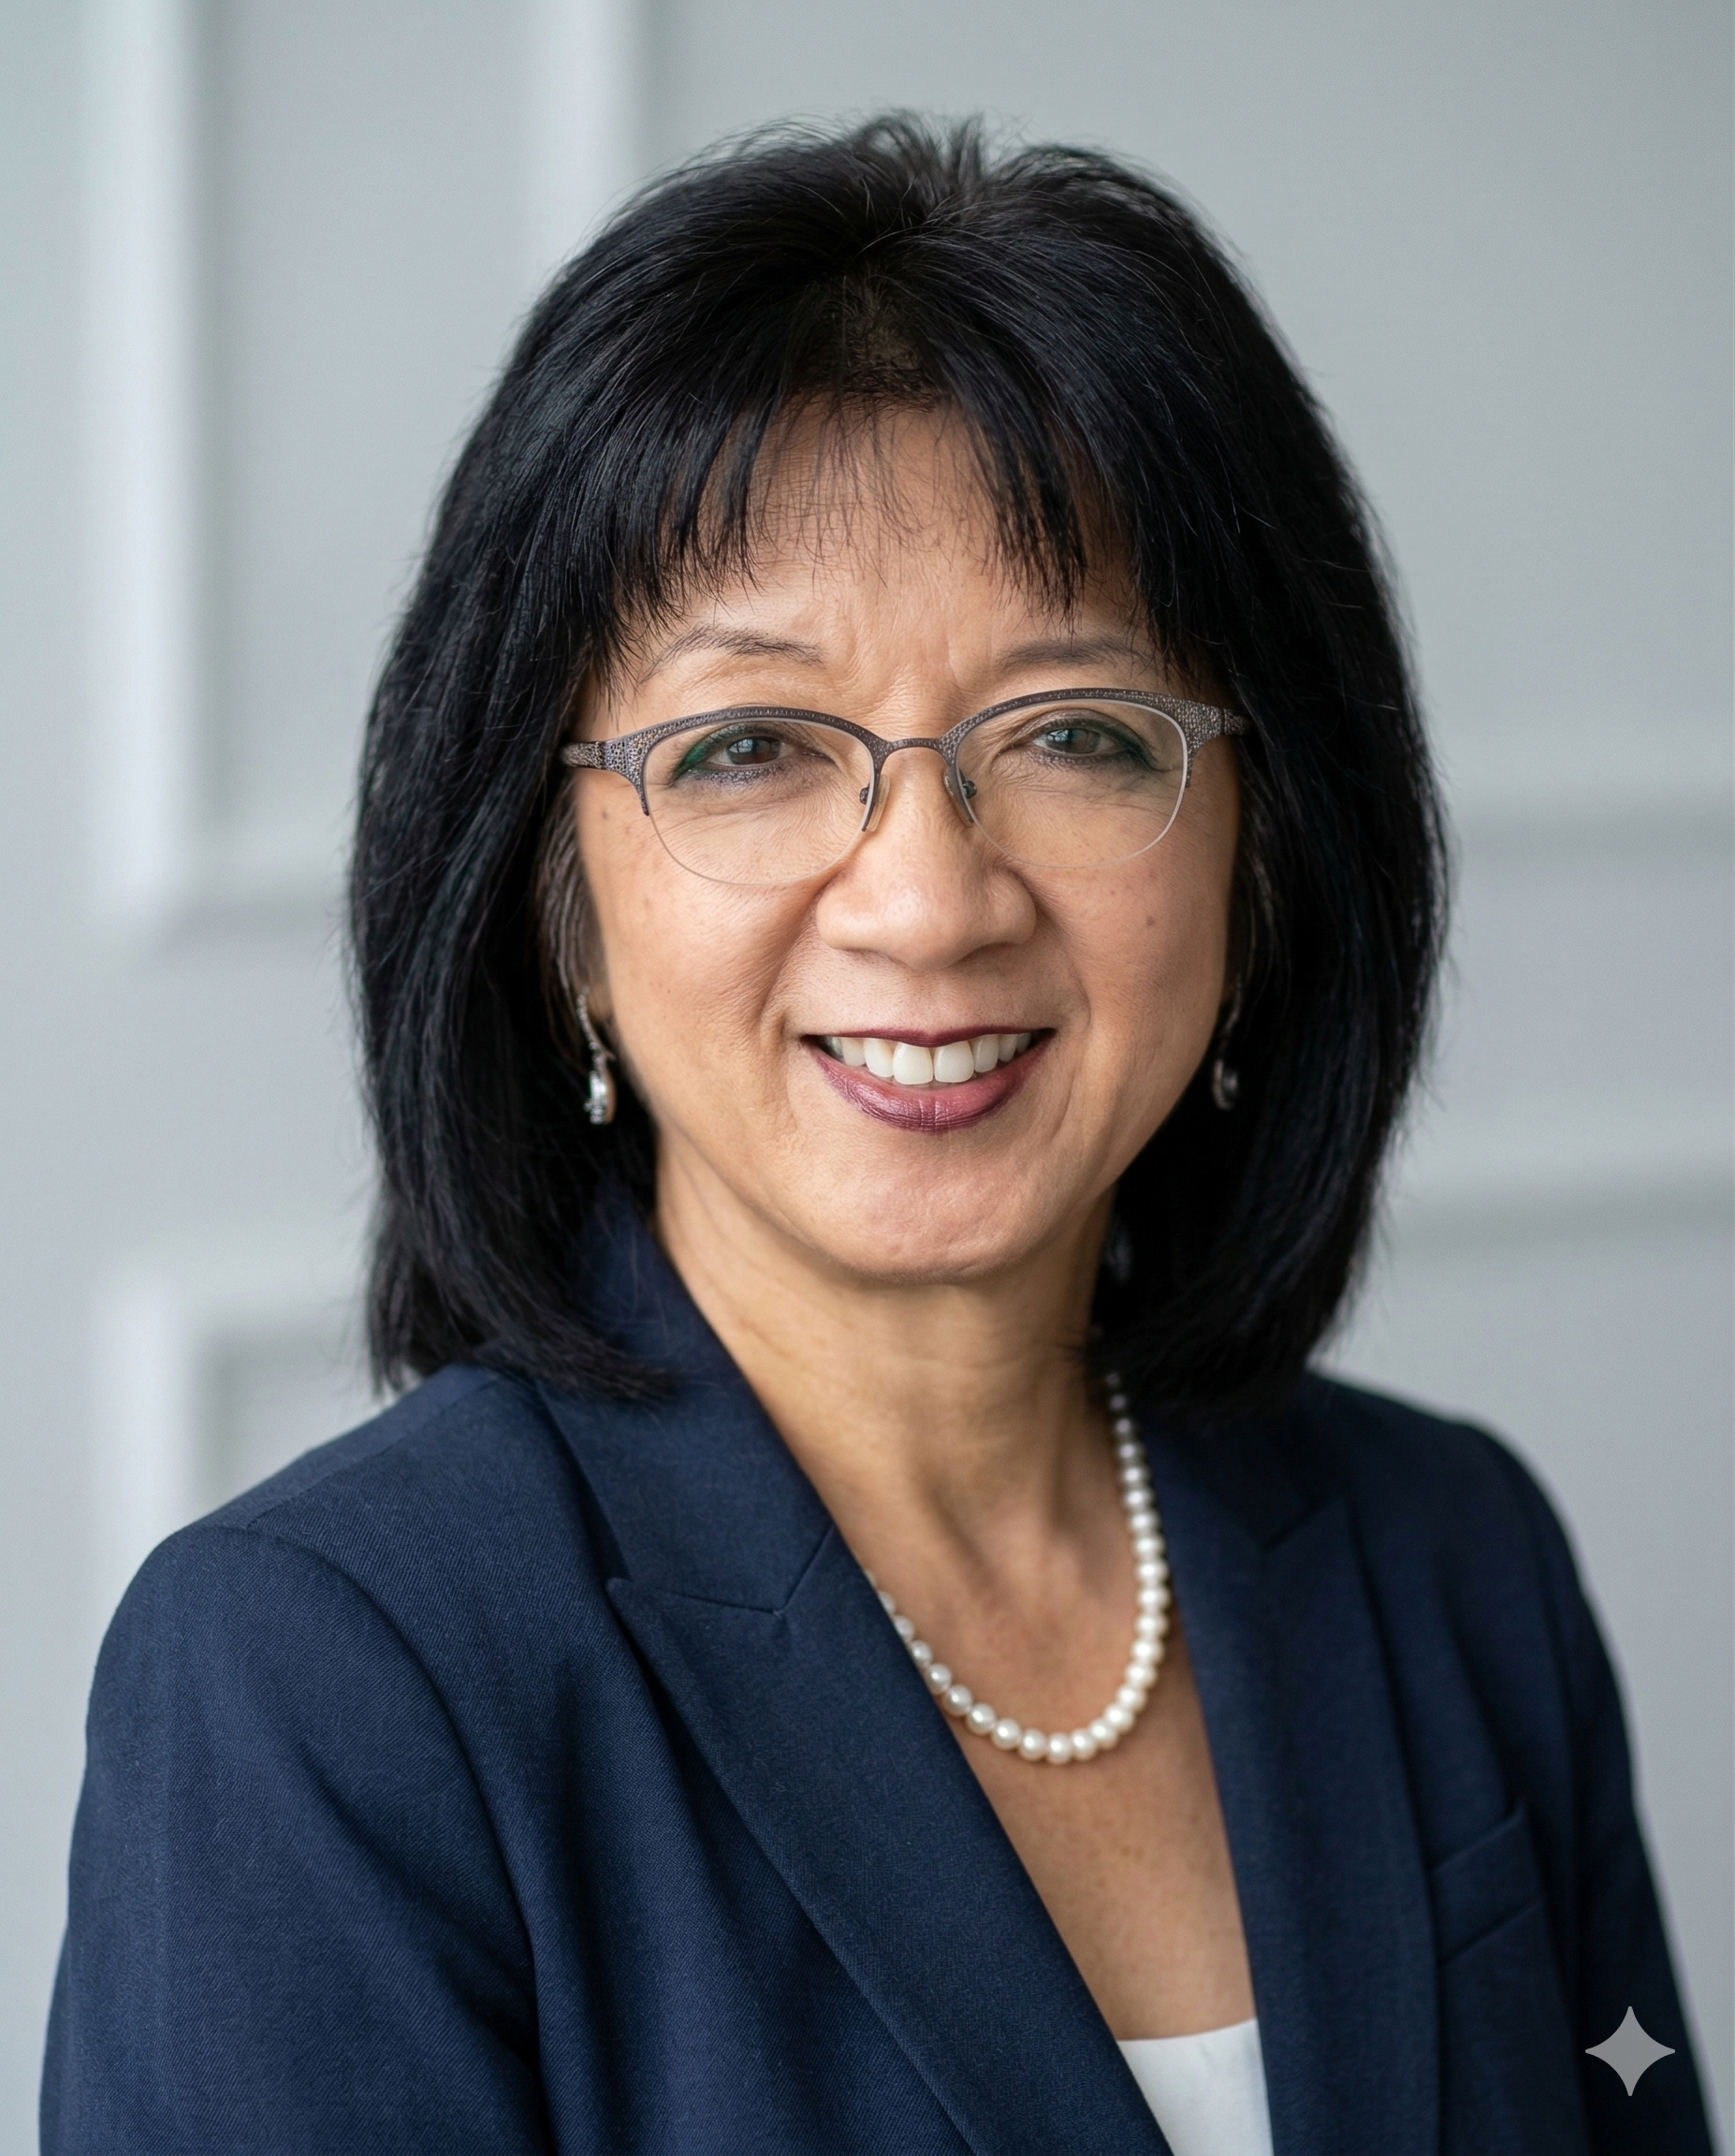 Elizabeth Wu, President, Cybersecurity Auditing Technologies
Bio: Elizabeth Wu is an IT consultant, IT security auditor, author, and President of Cybersecurity Auditing Technologies, with more than 25 years of hands-on experience working with technology, cybersecurity, and organizational risk. A contributor to the Center for Internet Security (CIS), her work focuses on the gap between what organizations believe about their cybersecurity and what can actually be demonstrated through evidence.
She advises leaders on cybersecurity governance, executive accountability, independent verification, and effective technology oversight. Elizabeth is the author of The Illusion of Cyber Governance: Why Proof Matters More Than Protection, which challenges organizations to move beyond assumptions and ask a fundamental question: How do you know? Her current work extends evidence-based assurance principles into AI governance and emerging technology risk.