Topic: The Ultimate Guide to Incident Response Governance
Abstract: Effective incident response is not just a technical exercise but also a governance imperative. As cyber threats become more sophisticated and regulatory expectations continue to evolve, organizations need clearly defined structures to ensure incidents are detected, escalated, managed, communicated, and reviewed with appropriate levels of accountability.
The current webinar explores the key elements of incident response governance, from establishing roles and responsibilities to defining escalation paths, decision-making authority, communication protocols, and regulatory reporting requirements. It will examine how organizations can align incident response processes with enterprise risk management and ensure that security, legal, compliance, privacy, communications, and executive teams can work together effectively during a crisis.
The session will also address how organizations can move beyond reactive response by using metrics, tabletop exercises, lessons learned, and continuous improvement to strengthen incident readiness and resilience. Join us to gain insights into building a governance model that enables faster, more coordinated decisions while providing the evidence and accountability needed for regulators, auditors, and senior leadership.
- Essential components of an effective incident response governance framework.
- Importance of clear roles, responsibilities, ownership, and decision-making authority during a cyber incident.
- Establishing effective incident classification, severity levels, escalation paths, and response triggers.
- Aligning incident response with enterprise risk management, business continuity, and crisis management.
- Strategies for coordinating security, legal, compliance, privacy, communications, and executive stakeholders.
- Preparing for regulatory notification, documentation, evidence preservation, and audit requirements.
- Incident response metrics and KPIs to measure readiness, response effectiveness, and resilience.
- Building a continuous improvement cycle using post-incident reviews and actions.
Speaker:
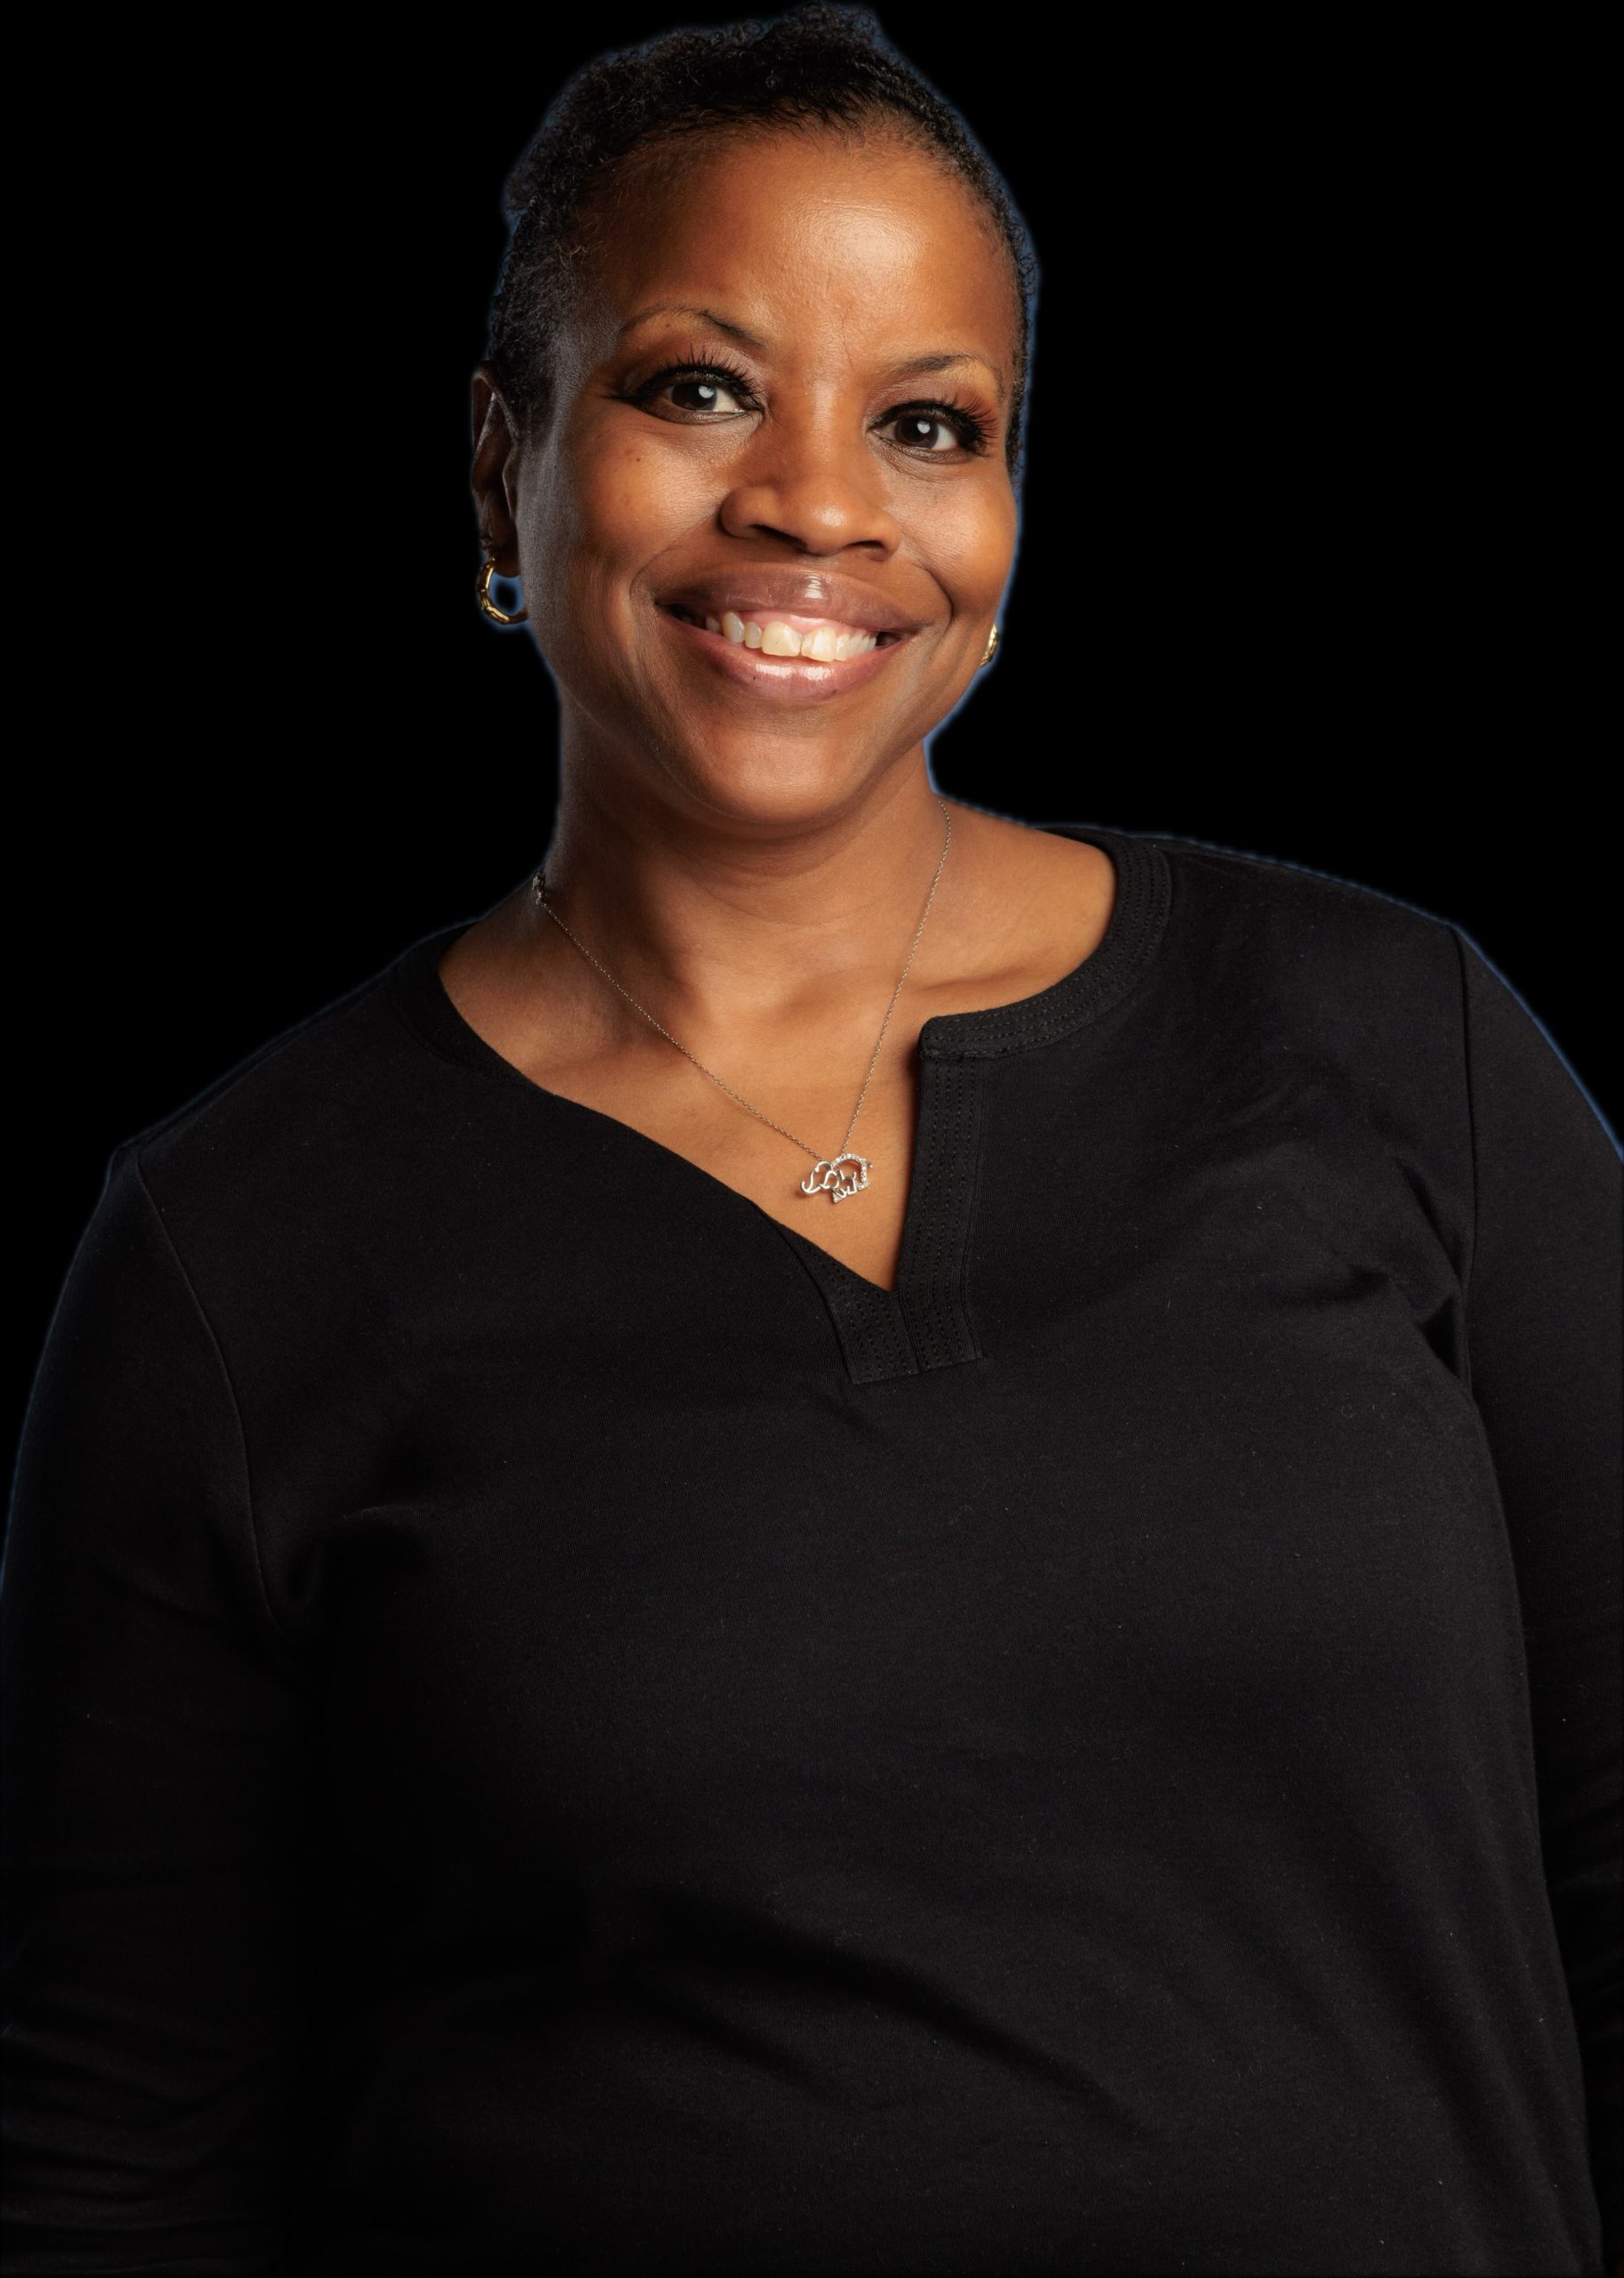 Mikini Williams, Founder and CEO, DAY1044 Solutions
Bio: Mikini Naomi Williams is a senior technology leader, certified AI consultant, and founder known for building durable systems, technical, organizational, and human, at the intersection of cybersecurity, artificial intelligence, and strategic execution. Drawing on more than 20 years of experience across government agencies, consulting firms, and enterprise organizations, Mikini brings both strategic depth and operational clarity to every engagement. She ensures that technology adoption is not only innovative but also governed, sustainable, and aligned with organizational objectives. Her approach to emerging technology, especially AI, is rooted in practical risk awareness, real-world execution, and a commitment to long-term value.
As the Founder and CEO of DAY1044 Solutions, she applies an operator’s mindset to every challenge, prioritizing outcomes that are measurable, defensible, and built to last. Her work centers on helping organizations, entrepreneurs, and institutions implement AI and security capabilities that respect constraints, protect trust, and enhance decision-making rather than replace it. She is particularly skilled at guiding nontechnical leaders through high-stakes technology decisions with confidence and fluency.